Close Menu
Şevket Ayaksız
    What's Hot

    AI watermarks could improve transparency but won’t stop AI slop

    Eylül 13, 2026

    LG’s 4K OLED gaming monitor gets a $600 discount

    Eylül 13, 2026

    Keychron’s 100-key macropad offers 8,000Hz polling for $65

    Eylül 13, 2026
    • software
    • Gadgets
    Şevket AyaksızŞevket Ayaksız
    • Home
    • Technology

      Apple: iPhone 17 and Older Models Hit With Unexpected $100 Price Increase

      Eylül 10, 2026

      Apple Watch Intelligence Could Be a Major Accessibility Breakthrough

      Eylül 10, 2026

      Apple May Skip the Base iPhone 18 This Year

      Eylül 10, 2026

      FCC changes robot vacuum rules, potentially affecting future models

      Ağustos 8, 2026

      Samsung’s new 2TB 990 SSD drops to its lowest price yet

      Ağustos 6, 2026
    • Adobe

      Adobe brings four key creative apps to Windows on Arm beta

      Ağustos 1, 2025

      Skip the Legal Jargon—Adobe Acrobat’s AI Reads Contracts for You

      Şubat 5, 2025

      Save 50% on a Top-Rated Adobe Alternative This Black Friday

      Kasım 30, 2024

      Save 50% on Adobe’s Creative Cloud This Black Friday

      Kasım 25, 2024

      Adobe Brings Generative AI to Premiere Pro for Smarter Video Editing

      Ekim 24, 2024
    • Microsoft

      Microsoft quietly removes Windows 11’s 32GB RAM recommendation

      Ağustos 6, 2026

      Microsoft aims to improve Windows 11 performance on 8GB PCs

      Ağustos 2, 2026

      Microsoft PowerToys remains an essential Windows utility

      Temmuz 31, 2026

      Microsoft says Windows Secure Boot certificate rollout is still in progress

      Temmuz 30, 2026

      Microsoft tests Windows Update changes after major outage

      Temmuz 29, 2026
    • java

      Optimizing Java Streams for High-Performance Applications

      Aralık 20, 2025

      AI Brings a New Spark to JavaScript Programming

      Kasım 9, 2025

      Revisiting the Spring Framework: What’s New and Why It Still Matters

      Kasım 9, 2025

      Top Highlights and Features to Watch in Java 25

      Kasım 3, 2025

      Mastering Java Cold Starts: Achieving High-Performance Serverless with GraalVM and Spring

      Kasım 3, 2025
    • Oracle

      JavaScript Community Pushes Back Against Oracle’s Trademark Claim

      Şubat 8, 2025

      Understanding the Impact of the Google vs. Oracle Decision

      Aralık 25, 2024

      Google Wins Legal Battle Over Java, Oracle Continues to Resist

      Aralık 25, 2024

      Oracle Unveils Verrazzano: A New Container Platform for Kubernetes

      Aralık 12, 2024

      Oracle vs. Google: Implications of the Verdict on Open Source Software

      Aralık 8, 2024
    Şevket Ayaksız
    Anasayfa » Securing REST APIs with Spring Security: A Comprehensive Guide
    software

    Securing REST APIs with Spring Security: A Comprehensive Guide

    By mustafa efeTemmuz 26, 2024Yorum yapılmamış3 Mins Read
    Facebook Twitter Pinterest LinkedIn Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Get Started with Authentication and Access Control in Spring Security: A Step-by-Step Guide

    Securing web applications is an inherently complex proposition. Spring Security offers Java developers a powerful framework for addressing this need, but that power comes with a steep learning curve.

    This article provides a concise overview of the essential components for securing a REST API with Spring Security. We’ll build a simple app that uses a JSON Web Token (JWT) to store the user’s information.

    JWT is fast becoming the standard approach to holding auth information because of its simplicity and compactness.

    A Simple Secure REST API

    Here’s what we want our simple app to do:

    1. Provide a UI with a button that sends a request to a back-end endpoint.
    2. Provide a username and password field for users to log in.
    3. If the API button is clicked and the user is not logged in, reject the endpoint call with an “HTTP 401 Forbidden” response.
    4. If the user is logged in, send them the response from the endpoint.
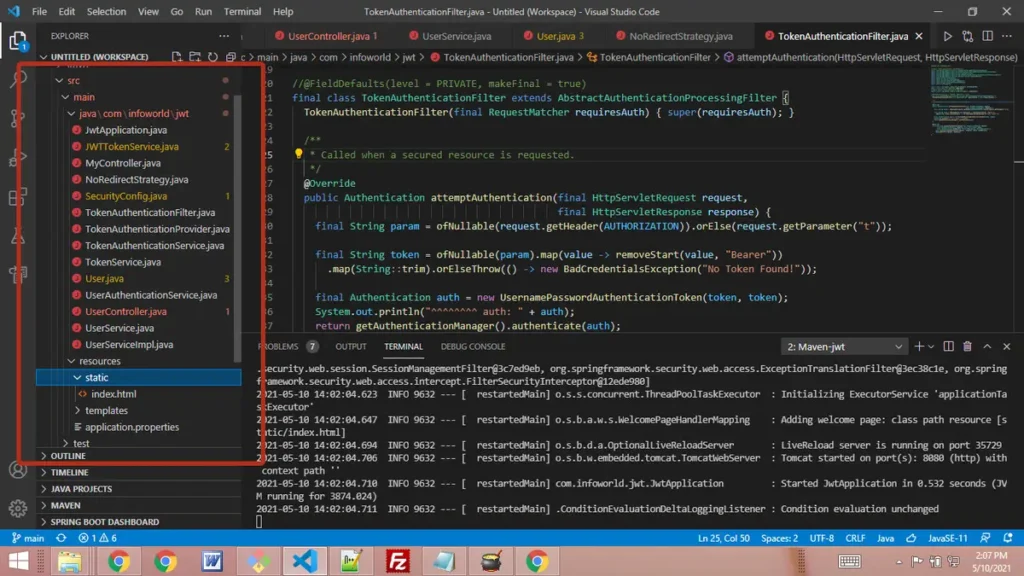


    This simple app will demonstrate all of the components required for using Spring with JWT to secure a REST API. The complete, operational version of the example app is here.

    Overview of Components

    1. Spring Security Configuration: Configure Spring Security to handle authentication and authorization. This involves setting up security filters, defining security rules, and customizing authentication providers.
    2. JWT Util Class: Create a utility class for generating and validating JWT tokens. This class will handle the encoding and decoding of JWTs, ensuring they are correctly formatted and secure.
    3. Authentication Controller: Implement an authentication controller that handles login requests. This controller will verify user credentials and issue JWT tokens upon successful authentication.
    4. Security Filters: Set up security filters to intercept incoming requests and validate JWT tokens. These filters will ensure that only authenticated users can access protected endpoints.
    5. User Details Service: Customize the user details service to load user-specific data. This service will interact with the user repository to fetch user information needed for authentication.

    Step-by-Step Implementation

    1. Spring Security Configuration:
      • Define security configuration class extending WebSecurityConfigurerAdapter.
      • Override configure(HttpSecurity http) method to set up endpoint security rules.
      • Add JWT authentication filter and exception handling for unauthorized access.
    2. JWT Util Class:
      • Create methods for generating and validating JWT tokens.
      • Use a secret key for signing and verifying tokens.
      • Include claims like username and expiration time in the token.
    3. Authentication Controller:
      • Implement a login endpoint that accepts username and password.
      • Authenticate the user and generate a JWT token if credentials are valid.
      • Return the JWT token to the client.
    4. Security Filters:
      • Create a filter to extract JWT from the request header.
      • Validate the token and set the authentication context.
      • Ensure unauthorized requests are blocked with appropriate responses.
    5. User Details Service:
      • Implement UserDetailsService interface to load user data.
      • Fetch user details from the database and return a UserDetails object.

    With these components in place, your Spring application will have a robust security mechanism using JWT for authentication and access control. This setup provides a solid foundation for building secure REST APIs.

    Post Views: 369
    java Programming Languages Software Development
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    mustafa efe
    • Website

    Related Posts

    AI watermarks could improve transparency but won’t stop AI slop

    Eylül 13, 2026

    Google lets Gemini users remove visible watermarks from AI images and videos

    Eylül 13, 2026

    OpenAI removes ChatGPT text chat limits for free and Go users

    Ağustos 8, 2026
    Add A Comment

    Comments are closed.

    Editors Picks
    8.5

    Apple Planning Big Mac Redesign and Half-Sized Old Mac

    Ocak 5, 2021

    Autonomous Driving Startup Attracts Chinese Investor

    Ocak 5, 2021

    Onboard Cameras Allow Disabled Quadcopters to Fly

    Ocak 5, 2021
    Top Reviews
    9.1

    Review: T-Mobile Winning 5G Race Around the World

    By sevketayaksiz
    8.9

    Samsung Galaxy S21 Ultra Review: the New King of Android Phones

    By sevketayaksiz
    8.9

    Xiaomi Mi 10: New Variant with Snapdragon 870 Review

    By sevketayaksiz
    Advertisement
    Demo
    Şevket Ayaksız
    Instagram
    • Home
    • Adobe
    • microsoft
    • java
    • Oracle
    • Contact
    © 2026 Theme Designed by Şevket Ayaksız.

    Type above and press Enter to search. Press Esc to cancel.