Close Menu
Şevket Ayaksız
    What's Hot

    AI watermarks could improve transparency but won’t stop AI slop

    Eylül 13, 2026

    LG’s 4K OLED gaming monitor gets a $600 discount

    Eylül 13, 2026

    Keychron’s 100-key macropad offers 8,000Hz polling for $65

    Eylül 13, 2026
    • software
    • Gadgets
    Şevket AyaksızŞevket Ayaksız
    • Home
    • Technology

      Apple: iPhone 17 and Older Models Hit With Unexpected $100 Price Increase

      Eylül 10, 2026

      Apple Watch Intelligence Could Be a Major Accessibility Breakthrough

      Eylül 10, 2026

      Apple May Skip the Base iPhone 18 This Year

      Eylül 10, 2026

      FCC changes robot vacuum rules, potentially affecting future models

      Ağustos 8, 2026

      Samsung’s new 2TB 990 SSD drops to its lowest price yet

      Ağustos 6, 2026
    • Adobe

      Adobe brings four key creative apps to Windows on Arm beta

      Ağustos 1, 2025

      Skip the Legal Jargon—Adobe Acrobat’s AI Reads Contracts for You

      Şubat 5, 2025

      Save 50% on a Top-Rated Adobe Alternative This Black Friday

      Kasım 30, 2024

      Save 50% on Adobe’s Creative Cloud This Black Friday

      Kasım 25, 2024

      Adobe Brings Generative AI to Premiere Pro for Smarter Video Editing

      Ekim 24, 2024
    • Microsoft

      Microsoft quietly removes Windows 11’s 32GB RAM recommendation

      Ağustos 6, 2026

      Microsoft aims to improve Windows 11 performance on 8GB PCs

      Ağustos 2, 2026

      Microsoft PowerToys remains an essential Windows utility

      Temmuz 31, 2026

      Microsoft says Windows Secure Boot certificate rollout is still in progress

      Temmuz 30, 2026

      Microsoft tests Windows Update changes after major outage

      Temmuz 29, 2026
    • java

      Optimizing Java Streams for High-Performance Applications

      Aralık 20, 2025

      AI Brings a New Spark to JavaScript Programming

      Kasım 9, 2025

      Revisiting the Spring Framework: What’s New and Why It Still Matters

      Kasım 9, 2025

      Top Highlights and Features to Watch in Java 25

      Kasım 3, 2025

      Mastering Java Cold Starts: Achieving High-Performance Serverless with GraalVM and Spring

      Kasım 3, 2025
    • Oracle

      JavaScript Community Pushes Back Against Oracle’s Trademark Claim

      Şubat 8, 2025

      Understanding the Impact of the Google vs. Oracle Decision

      Aralık 25, 2024

      Google Wins Legal Battle Over Java, Oracle Continues to Resist

      Aralık 25, 2024

      Oracle Unveils Verrazzano: A New Container Platform for Kubernetes

      Aralık 12, 2024

      Oracle vs. Google: Implications of the Verdict on Open Source Software

      Aralık 8, 2024
    Şevket Ayaksız
    Anasayfa » Strengthening the Foundation: Essential Security Best Practices for Every DevSecOps Team
    software

    Strengthening the Foundation: Essential Security Best Practices for Every DevSecOps Team

    By ayaksızAralık 20, 2023Yorum yapılmamış3 Mins Read
    Facebook Twitter Pinterest LinkedIn Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


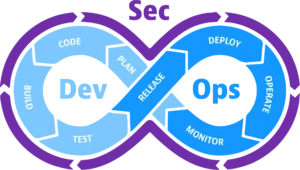
    Over a decade ago, Shannon Lietz coined the term DevSecOps with the vision of integrating security seamlessly into the IT development and operations landscape. The primary aim was to secure a dedicated seat for security at the table where IT developers and operators strategize. A decade later, it’s imperative to evaluate how far security has journeyed within the DevSecOps realm—whether the culture, practices, and tooling have matured sufficiently to facilitate the swift, reliable, and secure release of technology into production.

    The recently published SANS DevSecOps Survey serves as a beacon, shedding light on the significant traction gained by organizations in embracing security practices within their development workflows. Over 50% of respondents claimed to resolve critical security risks and vulnerabilities within an impressive seven days or less. However, the survey also reveals a paradox—while almost 30% of organizations deploy to production weekly, merely 20% assess or test for security vulnerabilities at a similar velocity. This disjunction raises questions about the alignment of development and security practices.

    In the journey toward mature security and continuous deployment, the adoption rates for DevSecOps practices highlight both progress and areas of improvement. Automation boasts a commendable 61% adoption rate, reflecting the industry’s commitment to streamlining processes. However, continuous integration (CI) lags slightly behind at 50%, indicating that many organizations are still navigating the path toward fully integrated development and security workflows.

    TABLE OF CONTENTS

    1. The Landscape of DevSecOps Practices

    • Shifting Left: The Evolution of Security in Development
    • The Paradox of Deployment Velocity vs. Security Assessment

    2. The Heart of DevSecOps: Top 3 Security Best Practices

    • Institute Security in API-First Strategies
      • APIs: The Cornerstone of Modern DevOps
      • API Security Trends: Insights from Wallarm’s API ThreatStats Report
    • Automate Code Scanning
      • From Manual Processes to Automated Vigilance
      • The Critical Role of Early Threat Detection
    • Standardize Data Observability Practices
      • From Application Logging to Modern Observability Tools
      • Extending Observability to Security, DataOps, and MLops

    3. The Nuances of Security Practices in DevSecOps

    • Navigating Over 25 Security Practices from the SANS Survey
    • Code-Based Methods: Adoption, Challenges, and Impact

    4. Expert Voices: Fundamentals of DevSecOps

    • Insights from Industry Leaders: Building Security into DevOps
    • Balancing Security Guardrails and Development Velocity

    5. Prioritizing Security Measures: Business Goals, Risks, and Compliance

    • Determining Which Security Practices to Prioritize
    • Aligning Security with Business Goals, Risks, and Compliance

    6. Beyond the Top 3: A Comprehensive Security Landscape

    • Third-Party Penetration Testing
    • Security Training and Awareness
    • Web Application Firewall (WAF) Implementation
    • Container Security Scanning and Cloud-Native Application Protection Platforms

    7. Continuous DevSecOps: The Call for Standardization

    • Addressing Risks Through Ongoing Security Practices
    • Building a Foundation for Continuous DevSecOps Excellence

    In conclusion, the journey of DevSecOps over the past decade reveals progress, challenges, and a call for continuous improvement. As organizations strive for a more secure and integrated future, the essay delves into key practices, expert insights, and the broader landscape of security within DevSecOps.

    Post Views: 452
    DevSecOps security
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    ayaksız
    • Website

    Related Posts

    AI watermarks could improve transparency but won’t stop AI slop

    Eylül 13, 2026

    Google lets Gemini users remove visible watermarks from AI images and videos

    Eylül 13, 2026

    OpenAI removes ChatGPT text chat limits for free and Go users

    Ağustos 8, 2026
    Add A Comment

    Comments are closed.

    Editors Picks
    8.5

    Apple Planning Big Mac Redesign and Half-Sized Old Mac

    Ocak 5, 2021

    Autonomous Driving Startup Attracts Chinese Investor

    Ocak 5, 2021

    Onboard Cameras Allow Disabled Quadcopters to Fly

    Ocak 5, 2021
    Top Reviews
    9.1

    Review: T-Mobile Winning 5G Race Around the World

    By sevketayaksiz
    8.9

    Samsung Galaxy S21 Ultra Review: the New King of Android Phones

    By sevketayaksiz
    8.9

    Xiaomi Mi 10: New Variant with Snapdragon 870 Review

    By sevketayaksiz
    Advertisement
    Demo
    Şevket Ayaksız
    Instagram
    • Home
    • Adobe
    • microsoft
    • java
    • Oracle
    • Contact
    © 2026 Theme Designed by Şevket Ayaksız.

    Type above and press Enter to search. Press Esc to cancel.